A Steady Mind and Disciplined Process: Miłosz Kaniewski on Building Secure Software
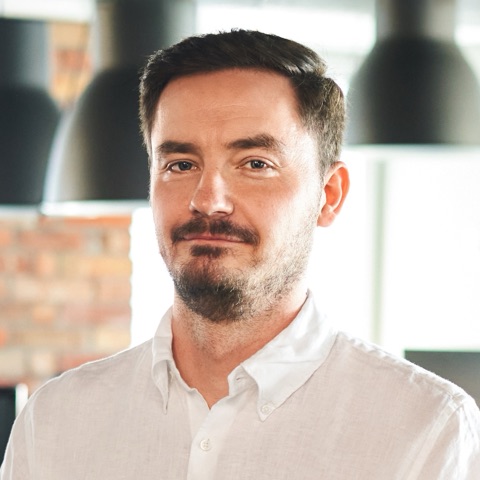
In deep-tech projects, it’s tempting to pursue every idea. Enterprise-grade software development demands engineering discipline, wise management of resources, and a reasonable approach to risk. Miłosz Kaniewski, Backend Development Team Lead at Fudo Security, works daily to ensure the product’s technological foundations keep pace with market challenges while giving engineers the best conditions to deliver reliable code.
Miłosz reveals what happens behind the scenes in software development: from managing ongoing work and keeping the platform up to date to session analysis driven by large language models, and even everyday digital hygiene and the boundaries of personal privacy.
From Writing C Code to Engineering Leadership
Miłosz entered the cybersecurity industry largely by pursuing technologies rather than following a specific career plan. He was interested in low-level C programming and Unix-like operating systems – a rare combination few companies in the Polish market offered at the time. One was Fudo Security (formerly Wheel Systems).
He began his career as a developer working on Lynx – a solution dedicated to TLS decryption. When that project was phased out, Miłosz shifted his focus entirely to the development of the Fudo Enterprise platform. Today, he heads the backend development team.
The company follows a structured pipeline from idea to production deployment. It starts with the market and customers, whose requests come through support tickets, Proof of Concept (POC) trials led by pre-sales engineers, partner networks, and the sales team. That feedback reaches product management and architecture, driving key business decisions and defining the initial technical blueprint.
Then the project reaches the development teams, split into smaller working groups of software developers, a QA tester, and a team lead. Running parallel to the backend, frontend developers work on the user interface.
“My primary role is to create an environment where engineers can work effectively. I make sure our teams have the right number of people with the necessary skills, and that they have everything they need to execute their tasks,” Miłosz explains.
Don’t Bite Off More Than You Can Chew
In engineering teams, the volume of ideas almost always exceeds available time. Requests come from diverse sources: direct customer feedback, internal optimization initiatives, and architectural improvements. Efficiency depends on rigorous selection.
“Customer requests never stop coming, as are our internal ideas for improvements. A major part of our job is filtering this stream to pinpoint what truly matters: what will deliver the greatest value to the company and genuinely enhance the product,” Miłosz emphasizes.
Experience has taught the team to stay grounded in their delivery capacity. Starting too many tasks at once creates bottlenecks and leaves no room to refine details.
“What counts is how many tasks we finish, not how many we start,” he adds.
Code Discipline and Resilient Architecture
Product resilience relies on an engineering stack that never falls behind. The product must remain current, and the technologies used cannot become a liability by falling out of common adoption. In cybersecurity, this directly impacts software resilience. Avoiding outdated components and tracking vulnerabilities continuously form the bedrock of defense.
Security responsibility cannot rest on individual shoulders or personal pressure. Instead, it rests on repeatable procedures and concrete architectural principles embedded directly into the codebase.
Fudo’s security architecture relies on core principles. Critical processes run in isolated environments (sandboxes) with minimal privileges, containing potential damage if an anomaly occurs. All stored data is encrypted by default with a key generated on the appliance during installation. Fudo Security never holds a copy of that key and has no way to access customer data. Furthermore, vendor support access is disabled by default. It requires the customer to explicitly enable it, plus a one-time password valid for a single login, and the customer can revoke access at any time.
Security That Doesn’t Get in the Way
A perpetual challenge in security software design is balancing strict protection with usability. Fudo’s architecture gives administrators the autonomy to configure security levels that align with company policy and environment requirements, including integrating with legacy systems that don’t support modern standards.
The engineers’ role is to make the most secure mechanisms the least disruptive to roll out. A prime example is the implementation of Two-Factor Authentication (2FA) based on one-time OATH (TOTP) codes. Instead of forcing administrators to manually generate and distribute QR codes to every user across a large enterprise, the process is fully automated. The QR code appears automatically on the user’s screen upon login, whether connecting through a web portal or directly via RDP or SSH protocols. Scanning it once in an authenticator app is all it takes to start working securely.
Administrators’ perception of PAM solutions is also shifting. Past concerns and the discomfort of feeling watched during routine work are giving way to an understanding of the tool’s true purpose. Recorded session metadata and replays exist for post-incident analysis, allowing teams to reconstruct the exact sequence of events in the event of an outage or security incident.
AI as a Watchdog for Privileged Sessions
The volume of privileged sessions and connections in vast enterprise environments makes manual human verification impossible. Fudo addressed this challenge by incorporating large language models.
Initially, the technology generated concise summaries of closed sessions, letting administrators review logs in seconds. In recent versions, Fudo added real-time analysis.
“An AI agent analyzes user actions after every executed command, classifying their intent on the fly,” Miłosz explains. If the activity stays within assigned privileges, the model logs its observations, leaving its reasoning accessible for later review. If a web server administrator suddenly probes database logs or modifies configuration files beyond their scope, the AI agent flags the anomaly in near real time. It can alert managers, pause the session, or terminate it immediately.
Data privacy remains critical. Fudo does not enforce a single AI engine; the client chooses which model handles analysis. Organizations can opt for major public cloud LLM providers, or connect an internally hosted model within their private network, retaining complete control over sensitive data.
Evolving Vectors of Cyberattacks
Recent high-profile security incidents, from attacks targeting healthcare networks and invoicing platforms to the manipulation of industrial cooling systems in European supermarkets, demonstrate the growing scale of cyber threats. Such operations are driven by financial gain and deliberate attempts to undermine public trust in institutions.
Artificial intelligence acts as a dual-use technology in this environment. While it empowers defenders, it also enables attackers to automate large-scale vulnerability discovery across codebases, replacing the manual labor of dozens of analysts.
When asked how regular users should navigate this environment, Miłosz advises healthy skepticism over panic:
“Fear doesn’t solve anything. We cannot simply walk away from technology today, just as we couldn’t abruptly turn off the power grid. From an individual’s perspective, the key is recognizing that security requires active participation. Taking a few moments for basic actions, like locking a national ID number in government registries or turning on multi-factor authentication, makes a tangible difference. At a societal level, continuous education remains the only lasting answer.”
Professional Habits Outside the Office
Years spent working in cybersecurity inevitably shape everyday habits, occasionally leading to humorous situations. Miłosz recalls a vacation on the Danish island of Bornholm, where a severe storm canceled ferry service back to the mainland:
“I was irritated that the ferry operator hadn’t sent me an SMS alert beforehand, leaving me on the island without accommodation. I called their customer service to complain, and the representative replied: ‘We would have loved to notify you, but in the booking form, you entered your phone number as 123456789.’ Uncompromising privacy defense sometimes comes at a cost,” he jokes.
How does the backend development lead summarize his role when talking to family and friends outside tech?
“I simply say that I work at a great company, alongside wonderful people, building high-quality tools that solve real problems. That is more than enough.”