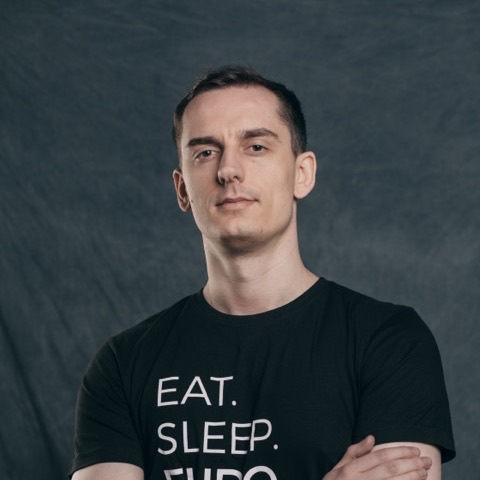
Behind the Scenes of Cybersecurity: A Conversation with Krzysztof Lenckowski, Head of QA at Fudo Security
He used to be interested in how systems are built and how vulnerabilities can be found in them. Quite quickly, however, he realized that while searching for vulnerabilities can be interesting, building attack-resistant solutions is a far more demanding task. Krzysztof Lenckowski, Head of QA at Fudo Security, joined the company at the beginning of 2021. Today, he ensures the quality of a product that supports security across industry, banking, and defense.
Before joining Fudo, he needed a change of environment and new professional challenges. He felt tired of the routine of repetitive manual testing in previous projects and was looking for a place where his work would have a more tangible impact on the business. Everything changed when he came across Fudo Security’s platform. The complexity of the product and the profile of the clients using it gave his testing work a deep sense of purpose. Krzysztof began testing with a clear goal: to help build solid, resilient software.
Here is how PAM tool development, product architecture management, and daily data security work look from the perspective of a Head of QA.
Responsibility for Product Quality and Release Challenges
Building software that critical corporate data security depends on carries significant responsibility. Krzysztof became particularly aware of this when he took on the role of Quality Assurance Manager.
“With every release, I felt like I was the one applying the ‘green checkmark.’ I’m releasing the company’s product to the outside world, acting as the gateway it must pass through,” Krzysztof recalls. “I kept asking myself: Did I do everything I could? Did we foresee potential issues? Did I focus where it mattered most?”
The early days could be stressful, especially when customers encountered upgrade issues. The complexity and scale of client environments were so vast that it wasn’t always possible to fully replicate them in the internal test environment. However, the QA team and developers drew key lessons from this. Through thorough process analysis and open communication with users, the update process was optimized. Today, bugs affect functionality, not causing system outages or upgrade blockers.
Release Predictability and the History of Solving Schedule Issues
Before Fudo reached its current level of release stability, the company had to address demanding market feedback. A few years ago, some clients pointed out a lack of predictability. Releases occurred at irregular intervals, and dates were sometimes pushed back.
How did Krzysztof and his team solve this issue? The key turned out to be better scope management.
“We were eager to respond quickly to every customer request. As a result, we took on more than the team’s current capacity allowed,” explains Krzysztof. From a business perspective, every new feature seemed urgent and necessary. The solution was to systematize the work: implementing tools to accurately measure team velocity and setting strict “decision gates” that were followed with iron discipline. Sometimes, ideas had to be postponed for later in the interest of higher schedule quality, which improved the predictability of new release delivery.
Major Platform Changes: RBAC and Password Vault
The evolution of an advanced software product often requires revisiting its foundations. A good example from Fudo’s history was the implementation of Role-Based Access Control (RBAC).
“It was one of the largest redesigns of the product. Previously, we had a few fixed roles with predefined permissions. We introduced the ability to define completely custom access controls for objects,” Krzysztof explains. While this overhaul required many subsequent refinements, further development of additional modules would have been impossible without it.
The changes introduced during the RBAC implementation made it possible to create the market-requested Password Vault. It was also one of the first major features the team approached using a new development framework featuring a dedicated team, comprehensive requirements analysis, and early beta feedback collection. Today, one of the biggest challenges for Krzysztof’s team is efficiently balancing such business projects with paying down technical debt.
PAM Tools: Market Evolution and Administrator Perception
Until recently, PAM tools were often perceived by administrators as uncomfortable control mechanisms, creating the feeling that someone was constantly watching over their shoulder. Today, that perception is changing.
“A good PAM solution is one the user hardly notices,” Krzysztof emphasizes. “Admins work as they always have, without feeling that their daily tasks are being blocked. The point is for the organization to have full visibility and an event history log for security purposes.”
The tools themselves have also expanded. They used to serve primarily to handle RDP or SSH connections. Today, in the era of cloud infrastructure and remote work, organizations choose to inspect a much broader range of traffic, including standard employees’ HTTP traffic. They want to ensure that corporate resources remain in the right hands.
Cybersecurity of Sensitive Data: Attacks, Practices, and Education
Observing recent security incidents – such as the alarming wave of attacks on healthcare providers and corporate invoicing platforms – it becomes clear that organizations often operate reactively. But what is the actual motive behind these high-profile breaches? Krzysztof points out that while financial gain or exploiting poorly secured data are common drivers, the broader geopolitical context cannot be ignored.
“We can never rule out that these are coordinated actions,” Krzysztof notes. “We know that governments often fund hacking groups to destabilize public opinion. It undermines trust in the system – the feeling that our state or our institutions are taking care of our well-being and our data.” In his view, creating this overarching lack of trust is often the primary goal of state-sponsored actors, with any financial and operational damage to the companies being merely a collateral bonus for the attackers.
This awareness of the global threat landscape underscores why defending against such attacks requires more than just reactive patching. Vulnerabilities frequently stem from technical debt, unmanaged access, and exposing legacy systems to the internet that were never designed for public exposure. To prevent these incidents and build resilience against both opportunistic hackers and coordinated groups, Krzysztof emphasizes several fundamental practices that every organization should adopt.
Starting with Data Mapping and Access Control
The absolute baseline of security is knowing where sensitive data resides and defining strictly who needs access to it. Simply handing out login credentials and relying on trust without ongoing verification is one of the most common security flaws. Organizations must map their data flows before assigning permissions.
Classifying Assets by Criticality
Not all data requires equal security controls. Security leaders must differentiate between routine operational information and critical assets. Protecting everything with the same intensity is inefficient; security measures and monitoring must focus heavily on high-risk areas and core systems.
Implementing Zero Default Access and Approval Steps
The best defense against social engineering and phishing is ensuring employees do not hold permanent access rights to critical systems. Access should be granted strictly on demand. Ideally, gaining entry to a sensitive database or server should require multi-person authorization or an explicit approval step.
Securing Legacy Infrastructure via Intermediaries
Krzysztof points to a concrete solution for legacy infrastructure: “If we have a legacy system containing sensitive data, we can secure its communications by monitoring traffic through a PAM solution. We don’t have to touch the legacy code. All verification and control happen inside a secure, attack-resistant intermediary tool.”
Replacing old systems is often costly or impractical, leading to dangerous workarounds. Instead of modifying legacy code, organizations can route traffic through a PAM solution. This creates a secure, monitored access layer, allowing safe external connections without altering the underlying, outdated software.
Focusing on Increasing the Attack Cost
Absolute invulnerability does not exist. The real objective of cybersecurity is to build layers of defense that make an attack so labor-intensive and expensive that it becomes economically unprofitable for threat actors. Proper access management is one of the most effective ways to raise that cost.
The Human Factor and Background Defense
The human factor remains a separate challenge. User education is difficult, and basic digital hygiene practices (like using password managers) are counterintuitive for many. As a result, situations still occur where employees write passwords on sticky notes attached to monitors or leave media containing confidential data in public places. Therefore, according to Krzysztof, the industry should design processes so that strict security policies are enforced in the background, relieving the burden on the end user (a great example being biometric authentication).
How Krzysztof Explains His Work to People Outside the Industry
Cybersecurity is a highly abstract field for anyone not dealing with it daily. How, then, does he explain the specifics of this work to outsiders, such as family members?
Krzysztof tries to rely on simple analogies: “I tell them that we build our own software running on a server inside another company. When that company wants to grant temporary access to an external specialist, our solution ensures that this access is secure. Additionally, it records everything that person does on the server, providing the company with a digital audit trail of the work performed.”
As he admits, people outside IT are often surprised that corporate systems even allow for such precise monitoring of every activity. Meanwhile, the job of Krzysztof and his QA team is to ensure these mechanisms operate flawlessly.